Independent Assurance for the Relyence Platform
Organizations rely on Relyence to manage information essential to their reliability, quality, and engineering processes. Our SOC 2 Type II report provides independent validation of the controls that protect this data and support the secure operation of the Relyence cloud platform.
Visit the Relyence Trust Center
What SOC 2 Type II Means
SOC 2 (System and Organization Controls 2) is an independent auditing framework developed by the American Institute of Certified Public Accountants (AICPA). It is widely recognized as a standard for evaluating how organizations protect customer data and maintain secure cloud services.
A SOC 2 Type II audit evaluates both the design of an organization’s security controls and how effectively those controls operate over time. The examination covered the Security Trust Services Criteria and included controls related to access management, encryption, system monitoring, vulnerability management, incident response, and more.
Why SOC2 Compliance Benefits You
Our customers use the Relyence platform to manage important reliability, quality, and compliance information. Protecting that data is a key part of how we operate.
Our SOC 2 Type II report independently validates that key security controls operated effectively throughout the audit period. These include:
- Role-based access controls
- Encryption of data in transit and at rest
- Continuous system monitoring
- Regular vulnerability scanning and independent penetration testing
- Documented incident response and security procedures
This assurance can help streamline security and vendor reviews when evaluating Relyence or supporting ongoing compliance requirements.
Access Our SOC 2 Report
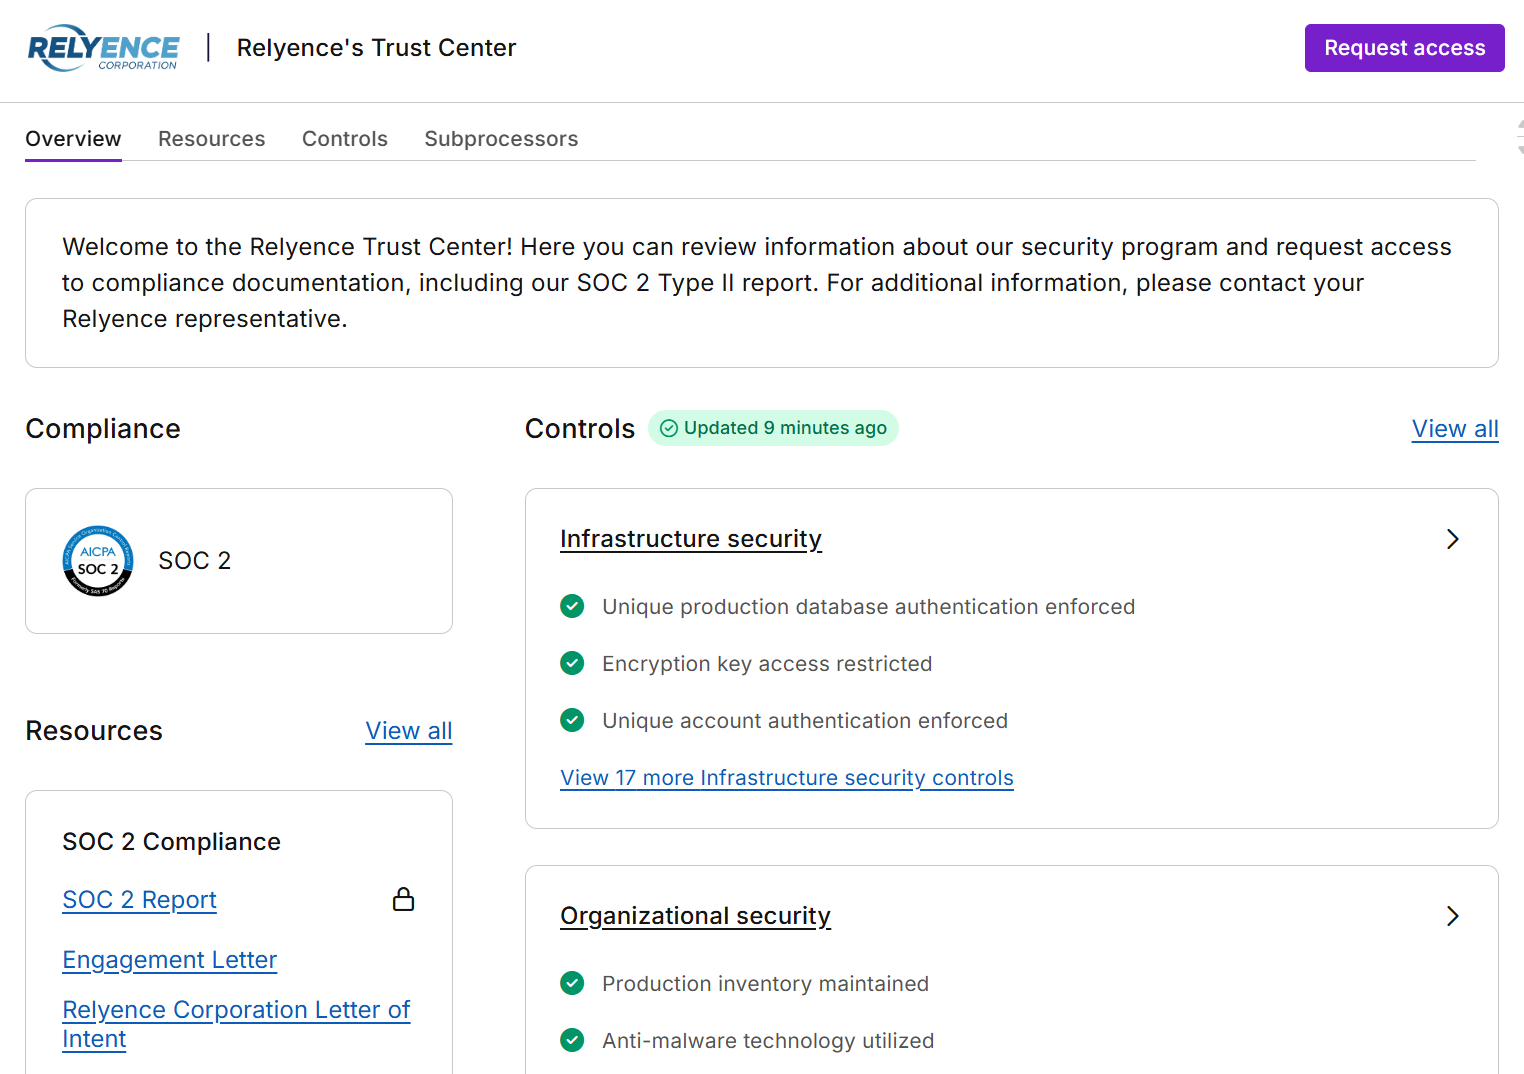
Current and prospective customers can request access to our SOC 2 Type II report through the Relyence Trust Center.
The Trust Center provides a central location to review available information about our security and compliance program and request access to supporting documentation. Certain materials, including our SOC 2 Type II report, may require approval and acceptance of a non-disclosure agreement before access is granted.
For questions about our security program or assistance accessing the report, contact us at wecare@relyence.com or speak with your Relyence representative.
